Blog Category
 Mobile App Testing(136)
 Web App Testing(11)
 Game Testing(24)
 Automation Testing(73)
 Security Testing(32)
 Performance Testing(15)
 Selenium(32)
 Test Management(15)
 Usability Testing(24)
 Guides and Tutorials(99)
 Best Practices(28)
 Expert Insights(20)
 Software Testing Events(4)
Our Services
- App Testing(136)
- Web App Testing(11)
- Game Testing(24)
- Automation Testing(79)
 Load Testing(9)
- Security Testing(32)
 Performance Testing(15)
 Hire a Tester(71)
Our Careers
7 Possible Security Testing Mistakes that Can Occur Anytime
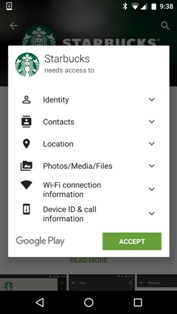
Mobile apps become a double- edged sword especially when a mobile payment application has to do mass transfers. New features are prone to hacking and extortion if not handled with care. NowSecure Mobile Security Report 2016 has found that 25% of the mobile applications always deal with at-least one highly extended security risk. When attacks on mobile applications increased, authorities started considering security checks before launching the app.
 Here, we are going to discuss about 7 possible security testing errors that may occur but can be avoided:
 We just can't do anything about it.
But!
A critical action plan can be implemented by:-
1. Monitoring the device, identifying every unusual activity
2. Appointing an in/out house team to identify and recover threats
3. Having policies that help you to limit the damages
Here, we are going to discuss about 7 possible security testing errors that may occur but can be avoided:
- Failing to understand how an application is exposed to risk
- Failing to connect security with application design
- Lacking the quality in security testing
- Use end-end encryption in data
- Exposing sensitive data
- Limit app features
- Develop a security response plan
We just can't do anything about it.
But!
A critical action plan can be implemented by:-
1. Monitoring the device, identifying every unusual activity
2. Appointing an in/out house team to identify and recover threats
3. Having policies that help you to limit the damages
Recent Posts
- Positive Vs. Negative Testing: Examples, Difference & ImportanceApril 22nd, 2024
- What Is Statement Coverage Testing? Explained With Examples!April 13th, 2024
- 60 Important Automation Testing Interview Questions & AnswersApril 2nd, 2024
- Verification vs. Validation: Key Differences and Why They MatterMarch 19th, 2024
- What is Compatibility Testing? Example Test Cases Included!March 18th, 2024